Antonio Beltran-Miller
Security Analyst · Detection & response
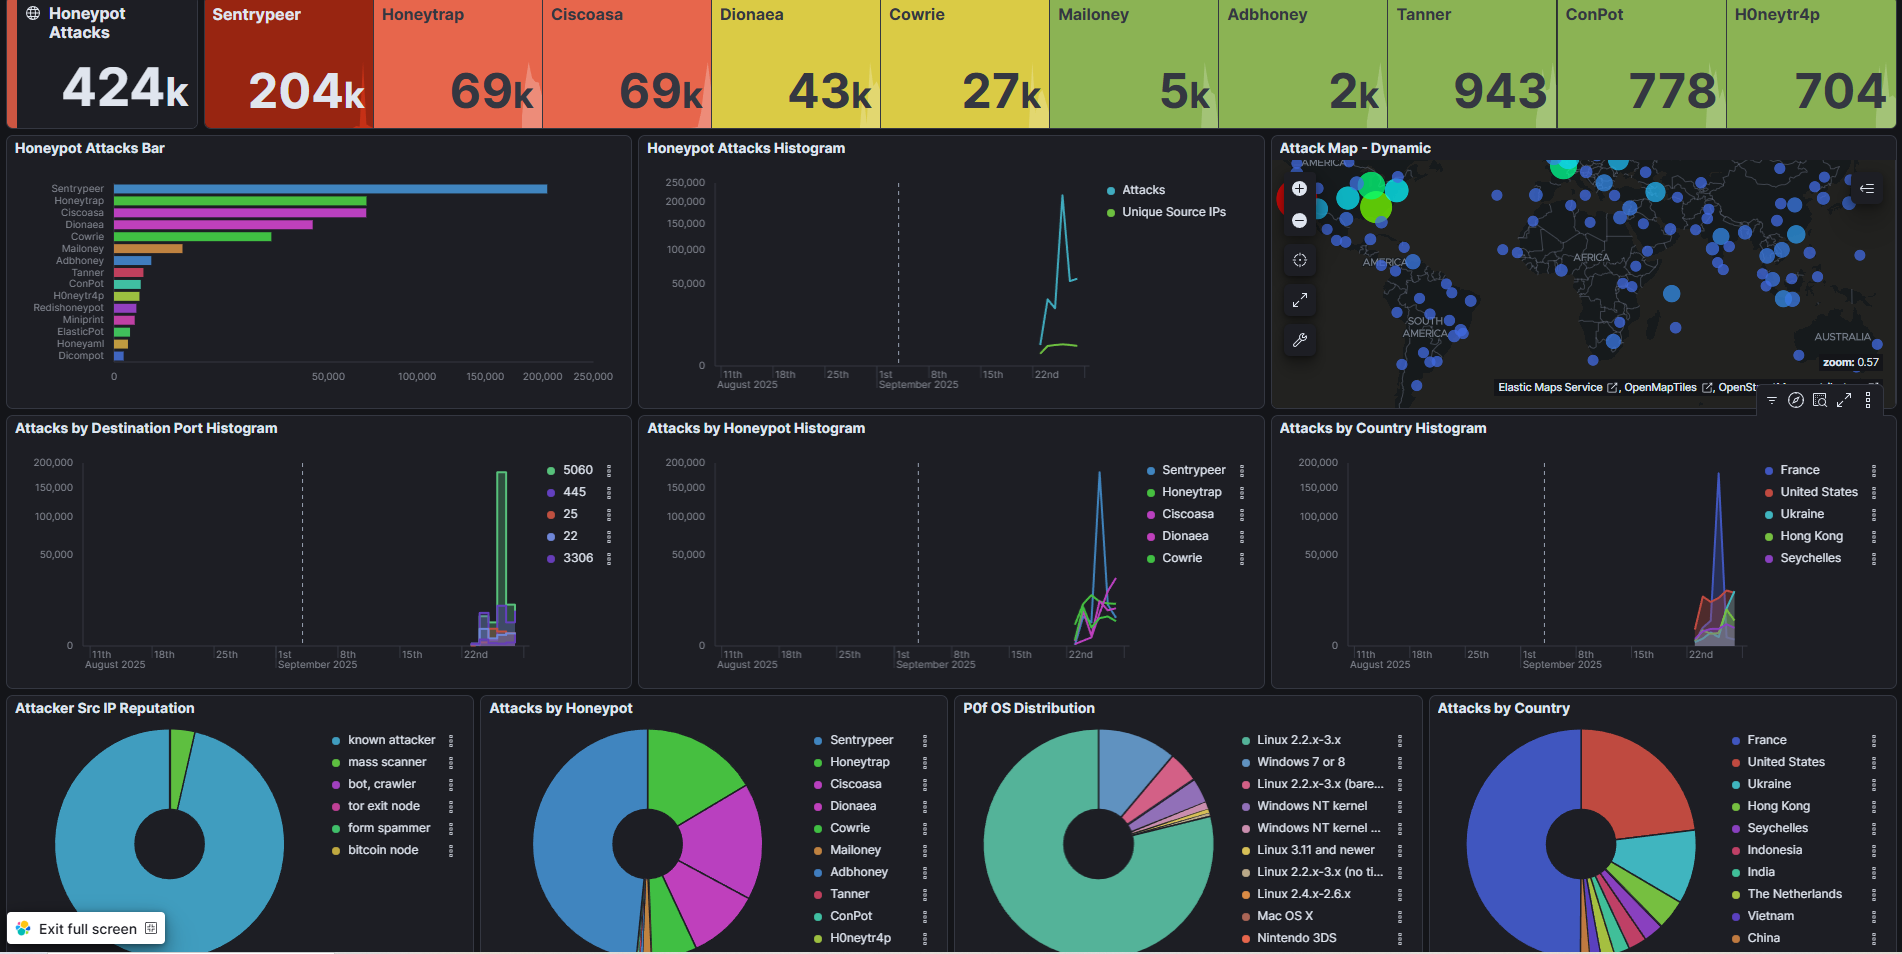
Security+ certified analyst focused on detection and response. I work alerts end to end, write and tune detections mapped to MITRE ATT&CK in a five-VM home lab, and ran a T-Pot honeypot to study live attack traffic.
Available for rotating and off-hours shifts · Onsite in the Detroit metro, hybrid, or remote
Start here
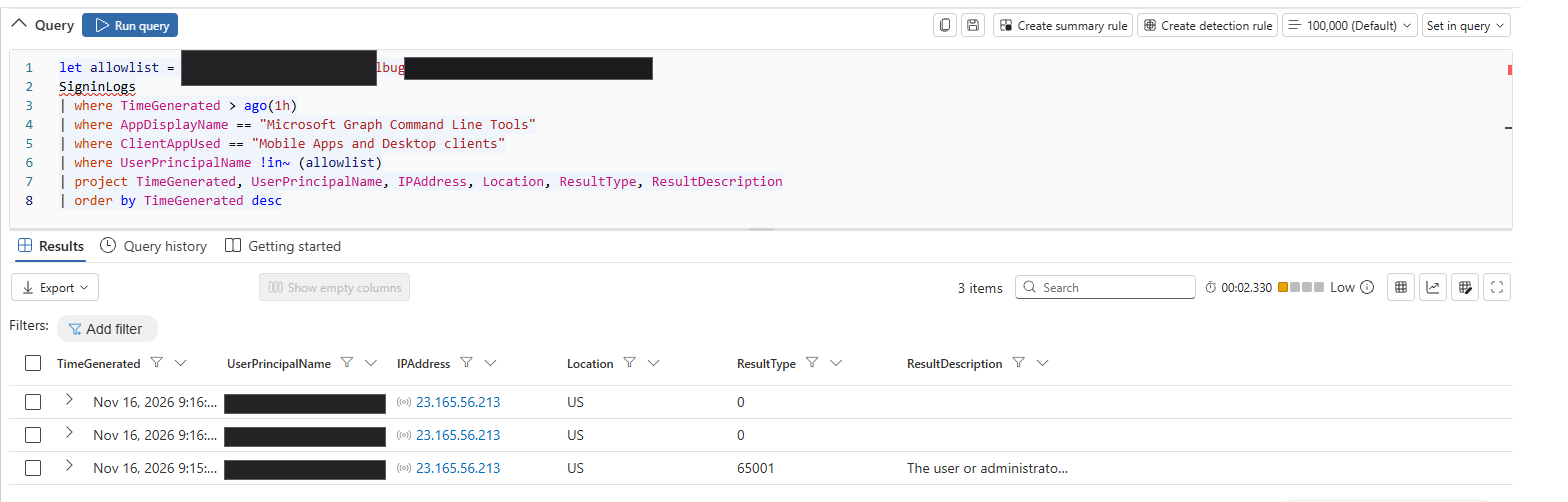
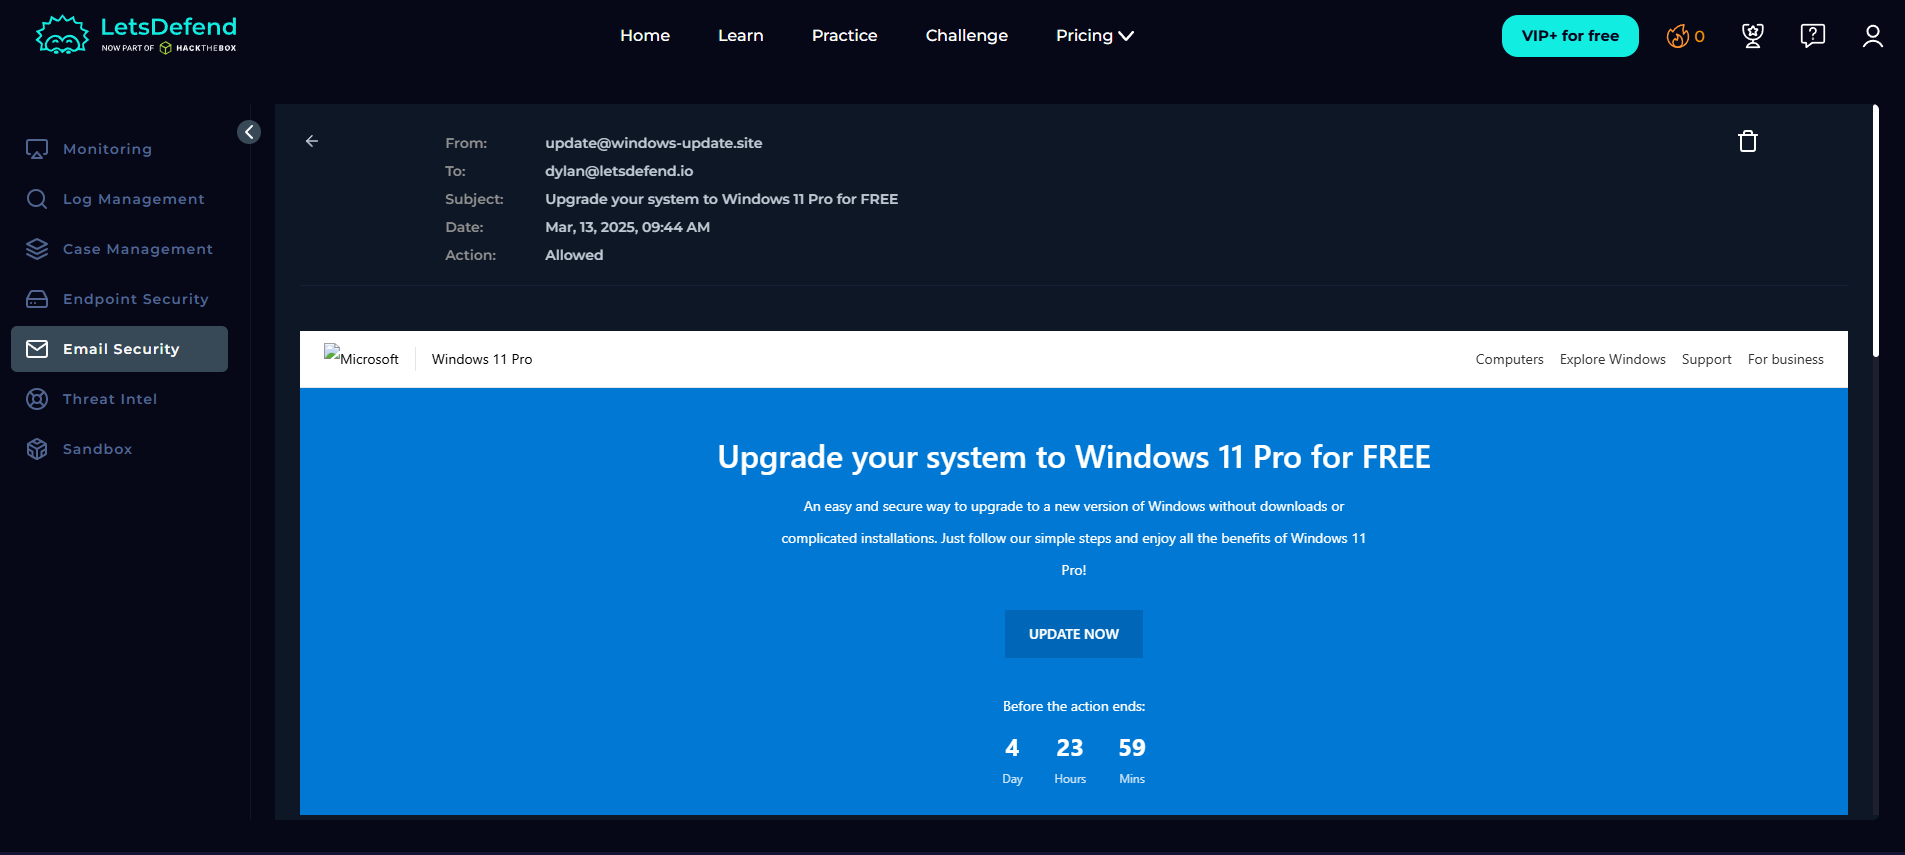
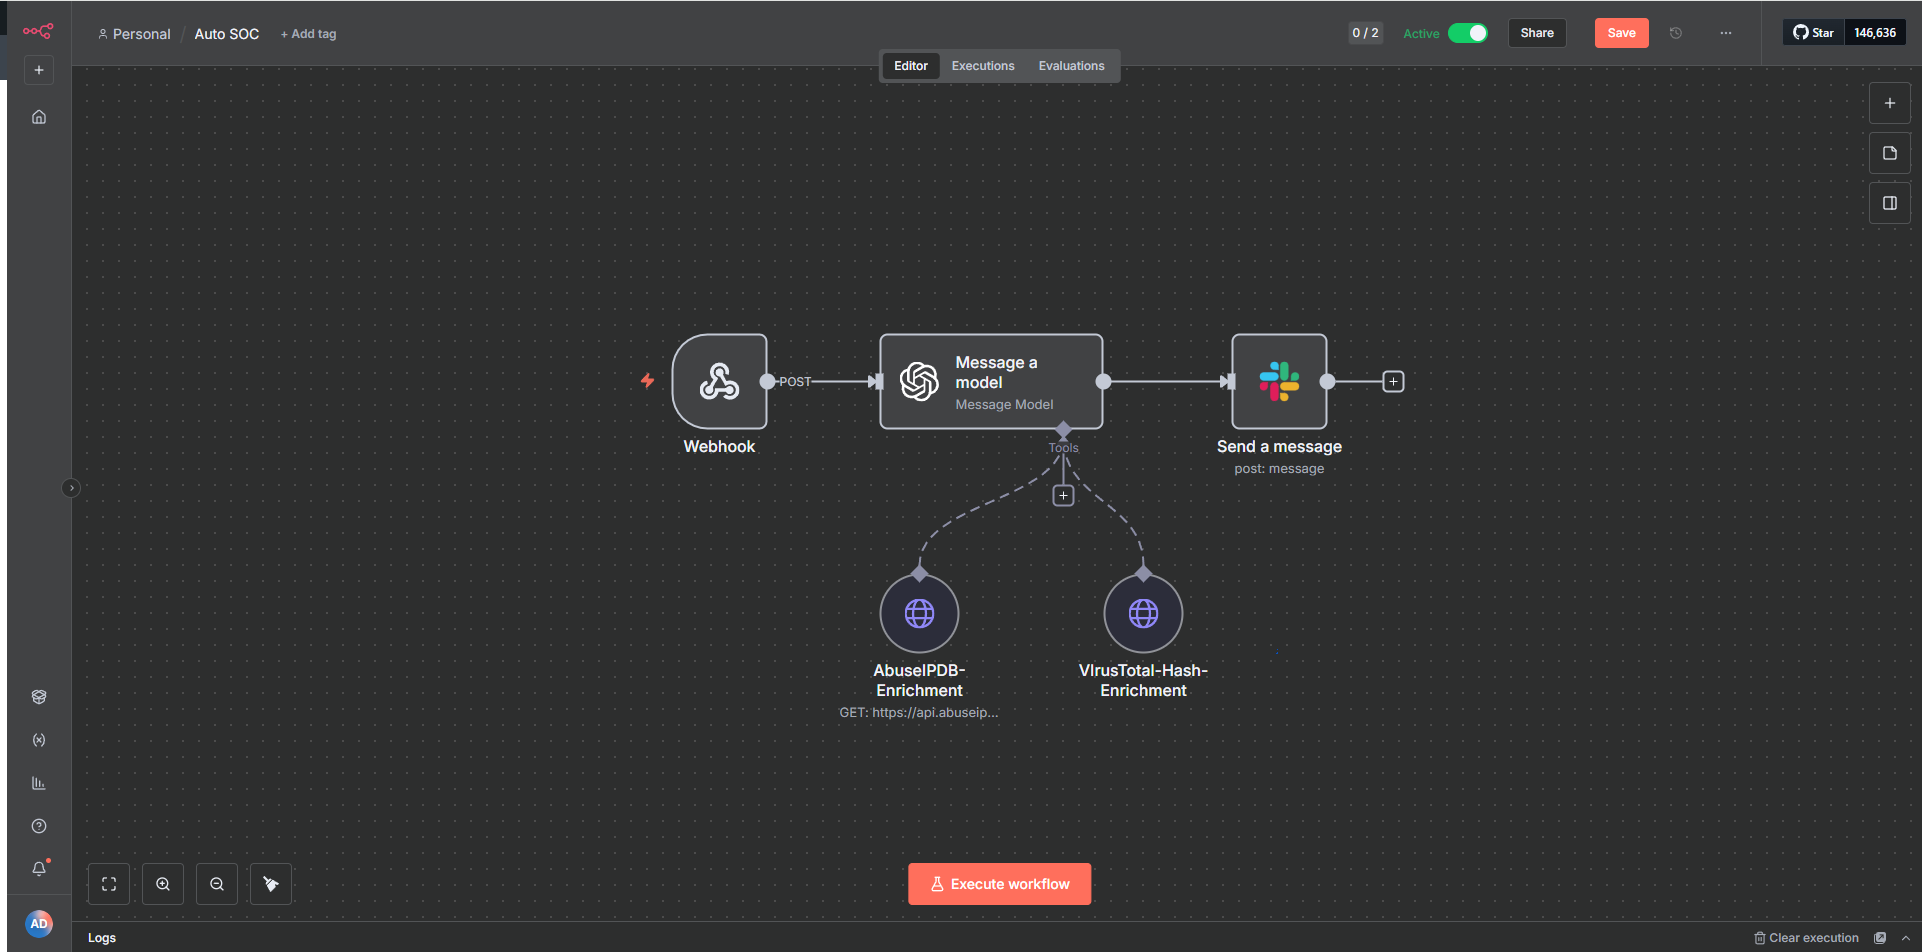
I spent about two and a half years as the only IT person for a 200-person logistics company, so I know what a normal Windows and Active Directory environment looks like and how to keep people working while something is broken.
Where I'm ready to contribute
Alert triage first, then the lab work behind it
A full alert investigation, the detection lab where I write and tune rules, and the honeypot where I study live attack traffic. Each one says what I built, what it was based on, and what the evidence shows.
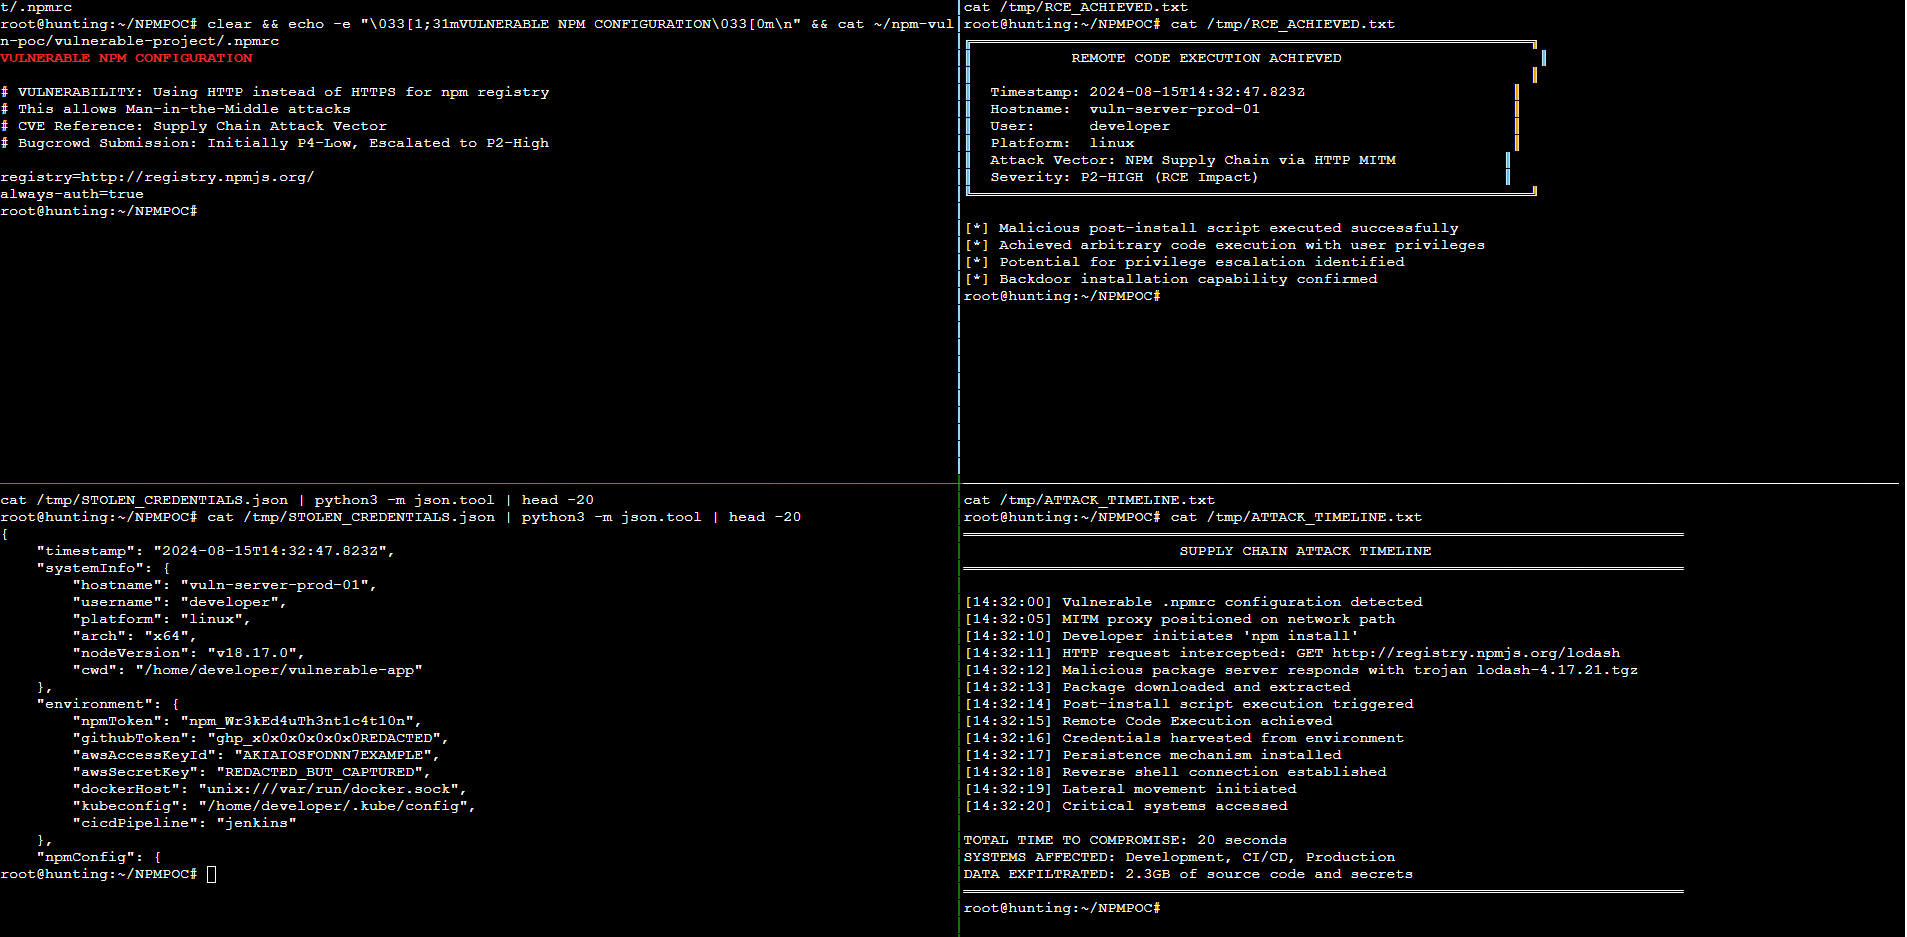
Other research: Blind XSS Capture Tool
Investigation write-ups
Short reports on real honeypot events and an incident response case. Each one ends in a verdict and the action taken, the way I would hand it to another analyst.
Tools I actually use
Every item links to the project, case, or credential where it shows up.
SIEM & detection
Security operations
Systems & cloud
Certifications
Verifiable where a badge exists.
CompTIA Security+
CompTIA
CompTIA CySA+
CompTIA
LetsDefend SOC Analyst Path
LetsDefend
Google Cybersecurity Professional
Coursera / Google
Also completed: Fortinet Certified Associate (August 2025) · Fortinet FortiGate 7.6 Operator (August 2025) · AWS Security Best Practices (2025) · SailPoint Identity Security Leader (2025)
Experience & education
My IT foundation is two and a half years as the sole IT resource at ALM Freight. From 2024 to 2026 I worked delivery full time while building the lab work above and studying for CySA+.
Dispatcher (sole IT resource)
ALM Freight
- ▸Only IT resource for a 200-person, two-site logistics operation with no dedicated IT department.
- ▸Managed 42 Android devices through 42Gears SureMDM and kept the Windows 11 workstations patched.
- ▸Administered Active Directory (user provisioning, account management, and group policy), and onboarded new employees from a standardized least-privilege Windows image.
- ▸Primary technical contact for 200+ drivers, resolving delivery-software and device failures in real time.
Delivery Associate
MMML (Amazon DSP)
Delivery Associate
DBE Logistics (Amazon DSP)
Assembly Technician
Contour Windows
B.S. Cybersecurity & Information Assurance
Western Governors University
Online · expected 2027
Contact
Let's talk
I'm looking for a SOC Analyst or detection role and I'm prepared for rotating shifts. Happy to walk through any of these projects live, including what I'd do differently.
Based in Ann Arbor, MI. Open to onsite in the Detroit metro, hybrid, or remote, and ready for rotating and off-hours SOC coverage.